
Multi-Tenancy Management
Multi-tenancy is available upon request for Enterprise customersReach out to the Sublime team to learn more.
Overview and terminology
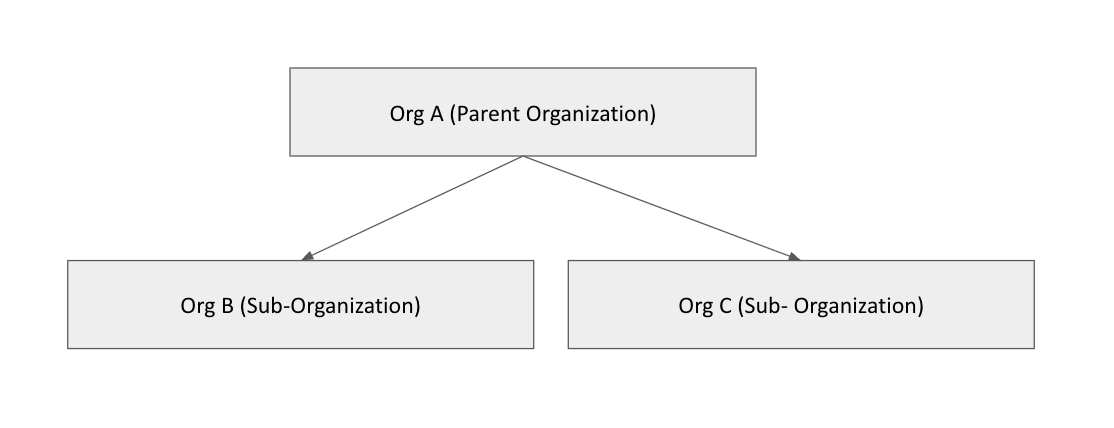
Multi-tenant management in Sublime allows you to connect organization A to organization B, organization C, and so on. When you sign in to organization A, you can:
- See all the organizations connected to organization A in the Sublime dashboard.
- Switch between any connected organization without re-authenticating.
Terminology
- A parent organization is an organization whose users can create and access other organizations without re-authenticating.
- A sub-organization is an organization whose parent organization can access it without re-authenticating.
- A standalone organization is an organization that is neither a parent nor a child organization.
Organization management
Supported deployments
We support Sublime Cloud and authorized Enterprise self-hosted AWS deployments.
Designating a parent organization
The Sublime team will configure an existing organization as a parent organization on request. Explicitly designating an organization as a parent organization protects against accidentally creating a multi-level hierarchy.
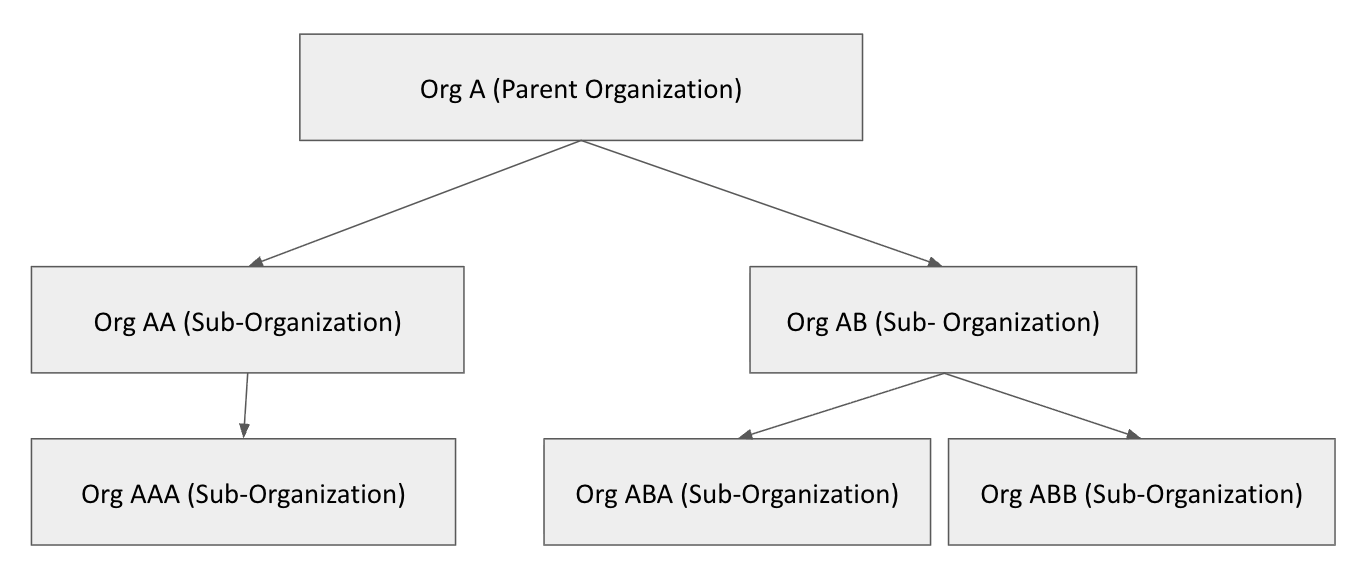
By default, sub-organizations cannot check sub-organizations.
On request, sub-organizations can have their own sub-organizations (up to two levels deep)The top-level parent organization can determine if a given sub-organization has the permission to create a sub-organization. Reach out to the Sublime team to learn more.
Creating child organizations
To create a sub-organization, use a Sublime API key created in the parent organization to make an API request like this:
curl -X POST \
  'https://YOUR_BASE_DOMAIN/v0/organizations/mine/child-organizations' \
  -H 'Content-Type: application/json' \
  -H 'Authorization: Bearer API_KEY_HERE' \
  -d '{"name": "My Sub Org"}'
The request body, formatted:
{
  "name": "My Sub Org"
}
Note that child organizations can only be created in the same Sublime instance as their parent organization, such as Cloud North America (platform.sublime.security).
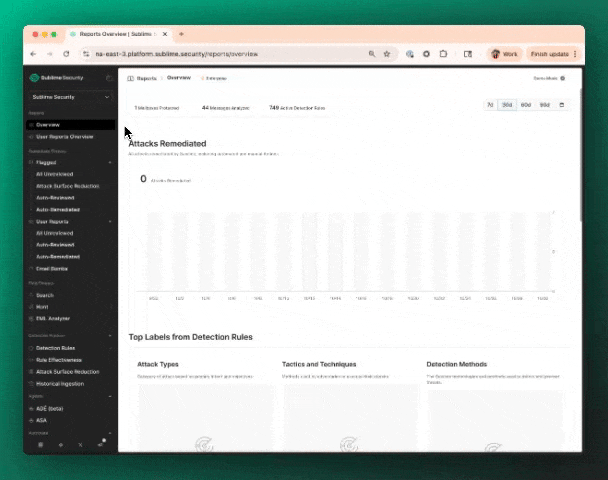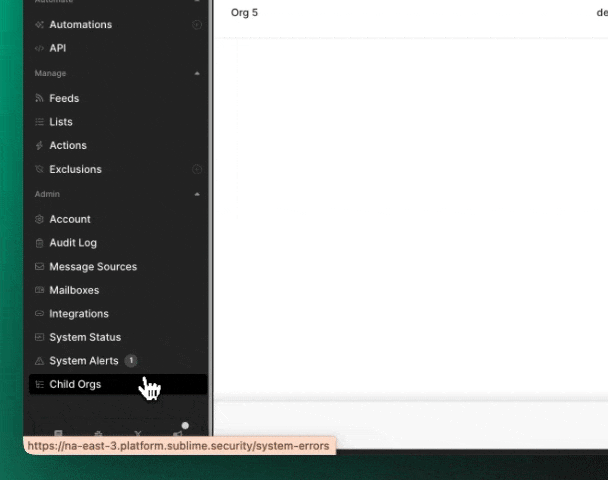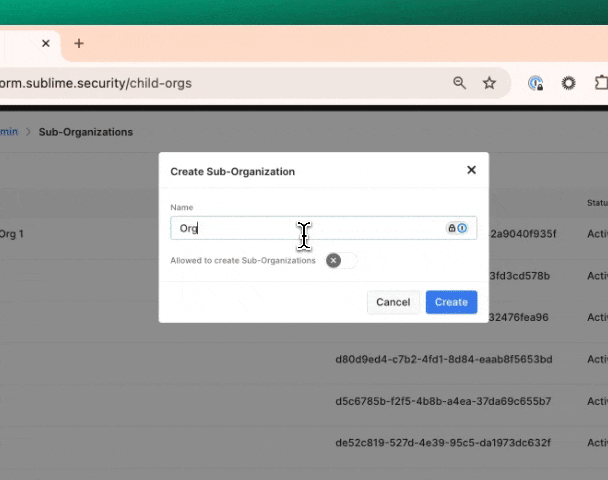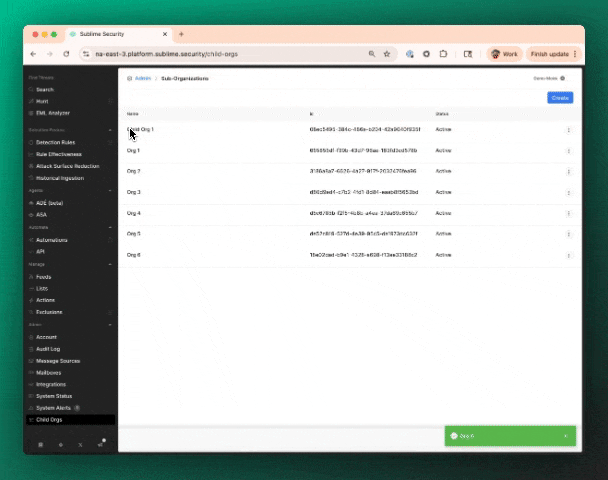
Parent organizations can also create new sub-organizations through the Sublime portal.
Turning existing organizations into sub-organizations
If you need an existing standalone organization turned into a child organization, contact the Sublime team.
Organization selection via query parameter
After signing in to your parent organization, you can programmatically select a sub-organization using the organization_id query parameter. For example, to load the Account page for an organization with ID d9dff3a5-ae7e-4afc-b0c4-84e264360315 in Cloud North America, you’d use this URL:
https://platform.sublime.security/account?organization_id=d9dff3a5-ae7e-4afc-b0c4-84e264360315
Deleting a sub-organization
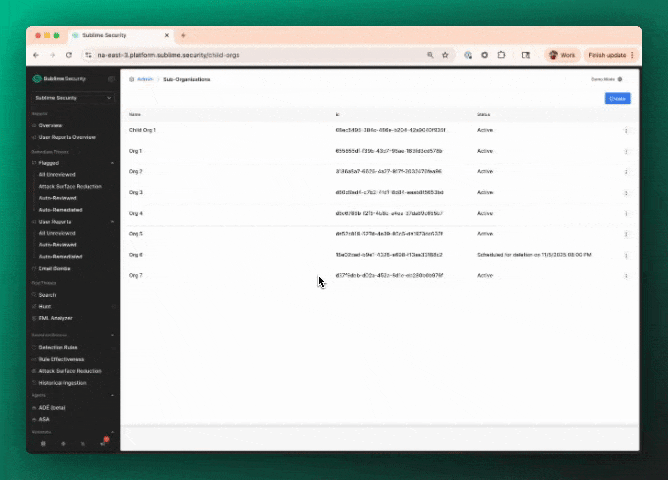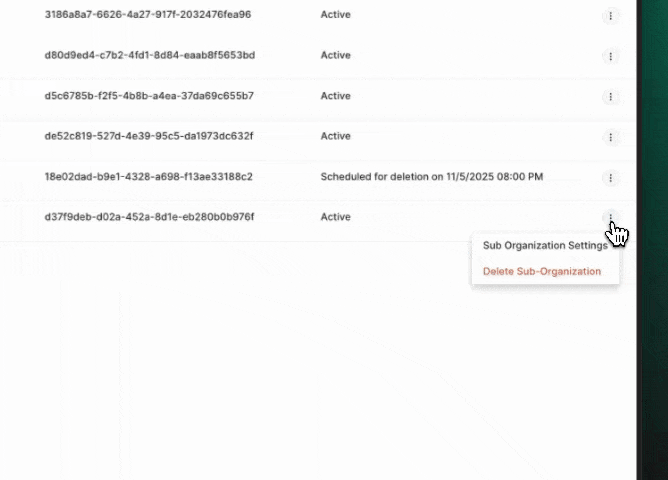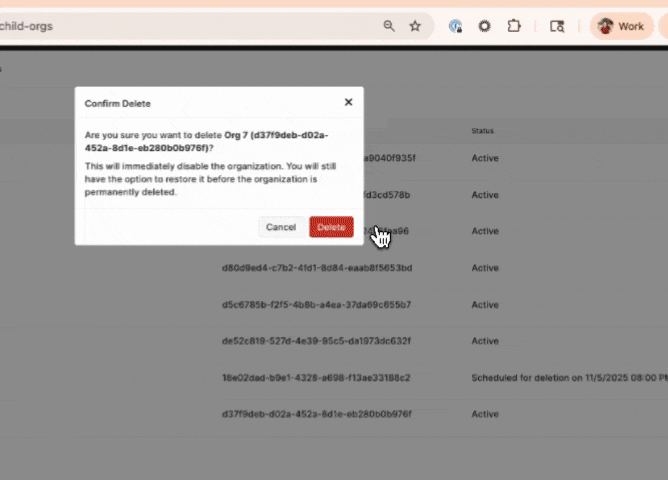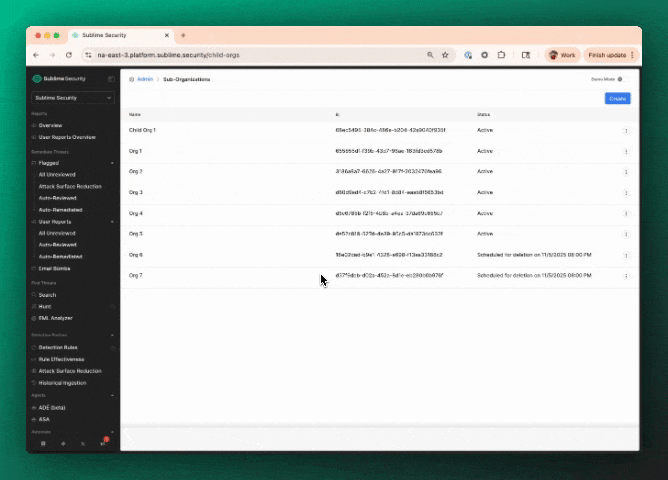
You can delete a sub-organization from the Sub-Organization page in the Sublime dashboard. You cannot delete a sub-organization that has an active sub-organization underneath it.
User management
Creating a user in a parent organization
To create a user in a parent organization, sign in to the parent organization and create a user under Admin > Account > Users, just as you would for a standalone organization.
Delegated access
Every user created in a parent organization automatically has access to every sub-organization under that organization, with the same role as they have in the parent organization. See Delegated users for details.
Accessing a child organization with a parent organization user
After signing in to a parent organization, you can switch to any sub-organization by clicking the current organization’s name in the left-hand sidebar and selecting the sub-organization in the searchable dropdown that appears.
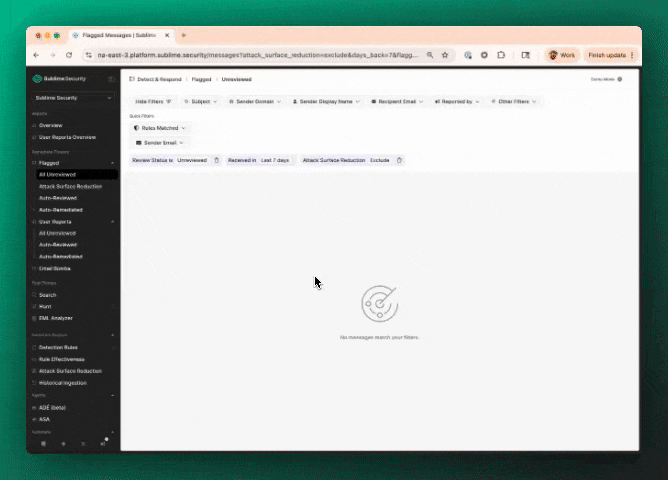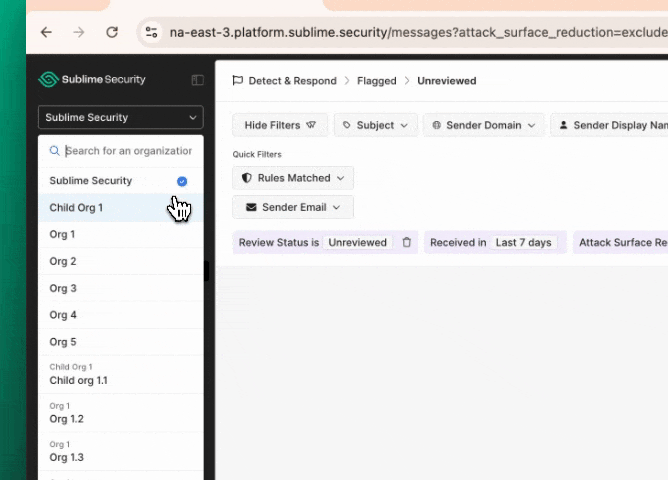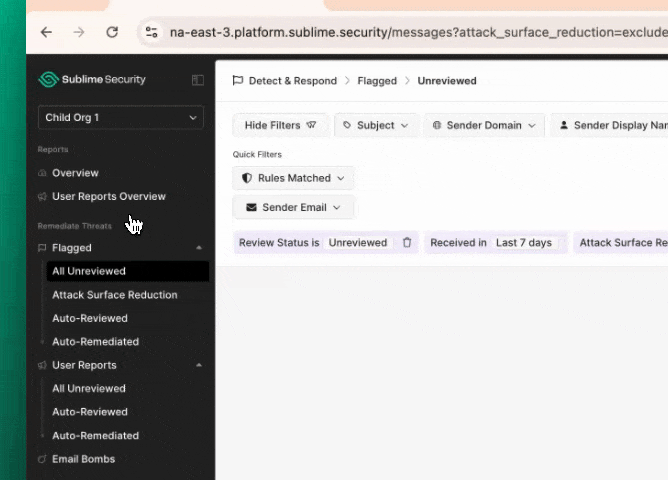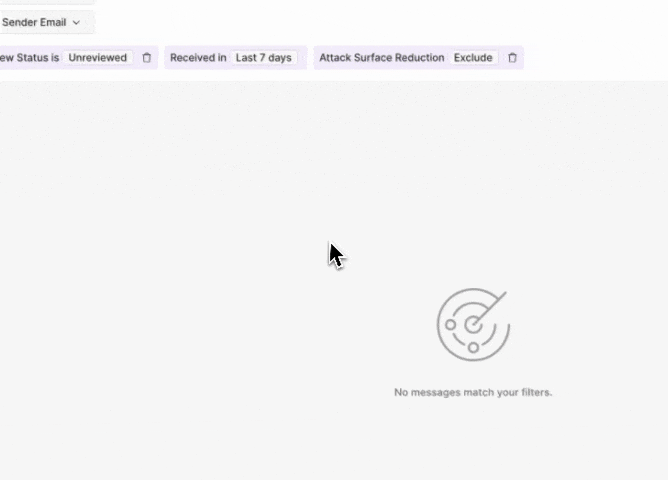
Organization selection is sticky per browser tab, so when you switch to an organization, all pages will load for that organization within that tab until you switch to another organization.
This stickiness allows you to work with multiple organizations at once in different tabs in the same window/browser profile.
Delegated users
When you switch between organizations, you are technically switching between different users (delegated users) in each sub-organization, all tied to your user in the parent organization. These delegated users:
- will always have the same role, name, and email as your user in the parent organization
- cannot be modified through the sub-organization
- can be modified by modifying your user in the parent organization, with any changes to that user propagating to delegated users in the sub-organizations
As delegated users are distinct users at the database and API level, users in different child organizations corresponding to the same user in the parent organization will have distinct user IDs in audit logs and any other context where a user ID is surfaced.
It is not possible to sign in directly as a delegated user, only to access a delegated user by first signing in to the corresponding user in the parent organization.
Creating a user with access solely to a child organization
To create a user that solely has access to a sub-organization, sign in to the sub-organization (directly or via a delegated user) and create a user under Admin > Account > Users, just as you would for a standalone organization.
Such a user may be used to, for example, give an end customer direct access to only their organization.
Single sign-on (SSO)
A parent organization and its sub-organizations each have separate SSO settings. For example, you can:
- Configure your MSSP’s SSO provider for the parent account so that your team can authenticate with the parent organization via that SSO provider and then access any child organization.
- Separately configure an end customer’s SSO provider for their child organization so that your customer can authenticate with only their organization via that SSO provider.
Updated 2 days ago